| Lesson 8 | The sqlnet.ora file to define Network Connectivity Options |
| Objective | Describe the characteristics of the sqlnet.ora file for an Oracle server running Oracle AI Database 26ai. |
sqlnet.ora File Characteristics in Oracle AI Database 26ai
sqlnet.ora is the Oracle Net profile file. It controls how Oracle software handles network connections, including authentication, connection checks, naming preferences, and diagnostics. It can exist on both database servers and clients. A setting matters only when the component making or accepting a connection reads and supports it.
This lesson focuses on the server profile. The file is not exclusive to shared servers, and it does not define your database tables, start a listener, or create dispatcher processes.
Separate the Three Network Configuration Files
- sqlnet.ora: Profile settings governing connection behavior.
- tnsnames.ora: Local aliases mapped to connect descriptors, including destination addresses and services.
- listener.ora: Listener configuration, such as listening addresses.
For example, changing a naming alias will not fix an authentication-policy mismatch. Likewise, increasing a timeout will not start a stopped listener. Identify which component is responsible before editing its configuration.
Confirm the active file location before making a change; multiple Oracle installations can have different profiles. See the preceding lesson on locating sqlnet.ora. Keep a backup and record which Oracle home and process environment use the file.
Authentication and Network Protection
Authentication establishes who is connecting. Encryption protects transmitted data, and integrity protection detects changes to that data. These are related but separate requirements: enabling encryption does not grant a user permission to log in or query a table.
SQLNET.AUTHENTICATION_SERVICES selects supported authentication services. SQLNET.ALLOWED_LOGON_VERSION_SERVER governs accepted authentication protocol compatibility; its number is not a database release selector. Choose settings for the actual client population and authentication design rather than copying an older installation's profile.
The following is an illustrative native network encryption policy, not a complete TLS configuration:
# Server-side native network encryption example
SQLNET.ENCRYPTION_SERVER = REQUIRED
SQLNET.ENCRYPTION_TYPES_SERVER = (AES256)
SQLNET.CRYPTO_CHECKSUM_SERVER = REQUIRED
SQLNET.CRYPTO_CHECKSUM_TYPES_SERVER = (SHA256)
REQUIRED makes the relevant protection mandatory. A client that cannot negotiate compatible protection cannot connect. Test the client drivers and supported algorithms before enforcing this policy. TLS over TCPS uses its own connection and certificate configuration; do not assume that the four settings above configure TLS.
For Oracle 26ai, do not copy obsolete TDE wallet-location examples into a new profile. ENCRYPTION_WALLET_LOCATION is desupported; TDE keystores use the documented WALLET_ROOT structure. TDE protects stored data and should not be confused with network encryption.
Connection Timeouts and Dead Connection Detection
Ask which stage of a connection you need to control:
- Opening TCP:
TCP.CONNECT_TIMEOUTlimits a client's attempt to establish a TCP connection. - Connecting and authenticating:
SQLNET.INBOUND_CONNECT_TIMEOUTlimits completion of the inbound database connection and authentication. - Checking an established connection:
SQLNET.EXPIRE_TIMEhelps detect a terminated or unusable connection.
These settings are not interchangeable. None is a general limit on how long a SQL statement may run. The listener also has a separate inbound timeout; coordinate it with the database-side setting rather than treating them as one timer.
# Illustrative server profile: review values for your environment
SQLNET.INBOUND_CONNECT_TIMEOUT = 60 sec
SQLNET.EXPIRE_TIME = 10
The explicit sec unit applies to the inbound timeout. SQLNET.EXPIRE_TIME is measured in minutes. A value of 10 configures connection verification, not a ten-minute idle-session limit. A healthy connection can remain idle and still respond to checks.
Oracle 26ai Dead Connection Detection
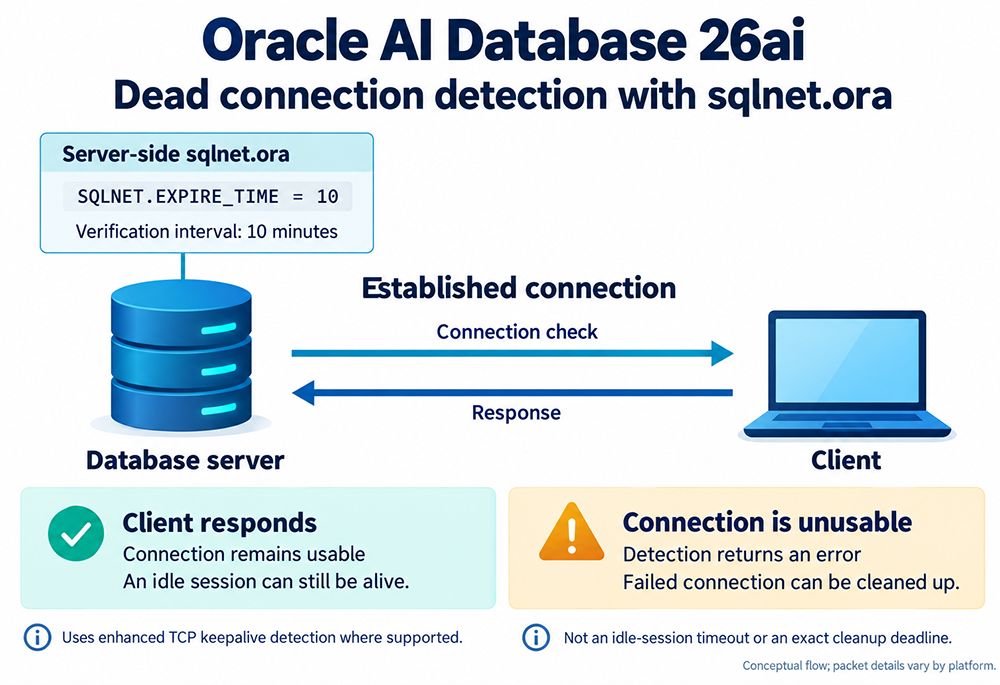
SQLNET.EXPIRE_TIME = 10 configures a verification interval in minutes. Oracle Net uses enhanced TCP keepalive detection where supported. A healthy idle session can remain connected: this setting is not an idle-session timeout or a guarantee of cleanup exactly ten minutes after a failure. The diagram shows a conceptual established connection, not listener routing or a shared-server process topology.
Consider a client whose computer loses power. The server may initially retain connection resources because it has not yet detected the failure. Dead connection detection helps identify that unusable connection. By contrast, a user who pauses between queries may still have a healthy connection. Do not use lack of SQL activity as evidence that a connection is dead.
Logging and Tracing: Account for ADR
The Automatic Diagnostic Repository (ADR) is enabled by default. It organizes diagnostic data into component-specific homes. Database, listener, and client diagnostics are not all one interchangeable sqlnet.log file.
# Keep ADR diagnostics enabled
DIAG_ADR_ENABLED = ON

# Enable temporarily when investigating a reproducible issue
TRACE_LEVEL_SERVER = ADMIN
With ADR enabled, legacy directory controls such as TRACE_DIRECTORY_SERVER and LOG_DIRECTORY_SERVER do not select the destination. Inspect the applicable ADR home instead. TRACE_LEVEL_SERVER remains relevant in ADR mode. Return tracing to the previous level after collecting the required evidence.
For deliberately configured non-ADR logging, the parameter names are LOG_DIRECTORY_SERVER and LOG_FILE_SERVER, without a SQLNET. prefix. Do not disable ADR merely to make an old directory example appear to work.
Server Settings Versus Outbound Client Settings
A database server can also initiate an outbound connection, for example through a database link. In that role it needs the appropriate client-side naming and connection behavior. This explains why a server installation may have naming settings without those settings controlling incoming listener traffic.
# Naming preference for software resolving an outbound connect identifier
NAMES.DIRECTORY_PATH = (TNSNAMES, EZCONNECT)
Read this as a naming-method preference, not as a list of database services. A local alias and the service name inside its connect descriptor can differ. Client drivers also vary in how they obtain configuration; verify the driver's documentation before assuming that an application reads the same profile as a command-line client.
In shared-server deployments, initialization parameters such as DISPATCHERS and SHARED_SERVERS establish the shared-server infrastructure. The network profile complements that infrastructure; it does not create a pool of shared servers. A connection failure should therefore be investigated at the relevant layer.
A Practical Verification Sequence
- Identify the symptom. Record the exact error, time, destination, service, and client driver.
- Locate the effective configuration. Confirm which profile the affected process uses, then save a rollback copy.
- Change one relevant setting. Keep authentication, encryption, timeouts, and diagnostics separate during diagnosis.
- Test a fresh connection. Follow the parameter's application requirements; do not assume an existing pooled connection will demonstrate a new setting.
- Check the evidence. Compare the outcome with database and listener diagnostics. Restore temporary tracing settings when finished.
For a no-listener error, inspect the listener and the requested host and port before changing SQLNET.EXPIRE_TIME. For a connection that reaches the server but fails authentication, investigate credentials and compatible authentication settings. A dead-connection parameter cannot repair either problem.
Lesson Summary
A useful server profile contains intentional, documented settings. Know which side of the connection uses each parameter, keep time units explicit, and inspect ADR before relying on legacy log paths. Use dead connection detection to identify failed connections, not to enforce user inactivity rules.
Master Tnsnames.ora File - Exercise
Practice distinguishing profile settings from connection aliases in the Master Tnsnames.ora File exercise.
Oracle 26ai References
- Oracle Net profile parameter reference
- Native network encryption and integrity negotiation
- Automatic Diagnostic Repository
- Oracle Net logging parameters